
Quick Takeaways
• The Akron-Summit County Public Library said on Wednesday, November 18, 2026, that attackers accessed cardholders’ names, addresses, dates of birth, phone numbers, email addresses and library card numbers through three of its vendors.
• The library’s app is unavailable, and all customers are urged to reset their account personal identification number (PIN) or password; the library does not store Social Security numbers, driver’s license numbers or credit card numbers.
• The library said its own systems are secure, its vendors contained the incident, and cybersecurity specialists are investigating.
AKRON, Ohio — The Akron-Summit County Public Library said on Wednesday, November 18, 2026, that it is investigating a cybersecurity incident in which attackers gained access to cardholders’ information, including name, address, date of birth, phone number, email address and library card number, the Akron Beacon Journal reported.
The incident involved three library vendors that provide services related to customer accounts, the library said in a statement posted on its website, according to the Akron Beacon Journal. Through those vendors, “an outside entity” accessed the information, the library told the Akron Beacon Journal.
The library emphasized that it does not collect or store such personally identifiable information as Social Security numbers, driver’s license numbers or credit card numbers, the Akron Beacon Journal reported. The attackers also did not access the library’s databases or customers’ borrowing history, according to the library’s statement as reported by the Akron Beacon Journal.
The library said it learned of the incident on Monday, November 17, 2026, the Akron Beacon Journal reported. In response, the library’s app is currently not available, and all customers are being urged to reset their personal identification number (PIN) or password for their library account, according to the Akron Beacon Journal.
The Akron-Summit library said its systems are secure and that its vendors took immediate steps to contain the incident and secure the district’s systems, the Akron Beacon Journal reported. The vendors engaged third-party cybersecurity specialists to investigate the cause and strengthen protections, according to the Akron Beacon Journal.
The cybersecurity incident has affected several libraries and vendor systems across the country, the Akron-Summit statement said, according to the Akron Beacon Journal. The neighboring Cuyahoga County Public Library also confirmed this week that attackers accessed patron account information through its vendors, the Akron Beacon Journal reported — a breach NewsForce247 covered in its report on the Cuyahoga County library breach. The week also brought a separate technology incident to a Stark County school district, covered in NewsForce247’s report on the Perry Local Schools closure.
The library urged customers to watch their library accounts and report any unusual activity to the library, the Akron Beacon Journal reported. Customers should reset their PIN or password for their library account, and the library said strong PINs and passwords offer the best protection when they include a capital letter, a lowercase letter, a number and a special character, and are at least 12 characters long, according to the Akron Beacon Journal.
Updating a library account PIN or password will not update third-party library services such as Libby and Hoopla, the library said, according to the Akron Beacon Journal. Customers who reset their PIN or password will need to do so in Libby and Hoopla as well, and customers can reset their PIN or password now by signing into their account, the Akron Beacon Journal reported.
The Akron incident is part of a wider run of technology disruptions hitting Ohio public institutions this month. Government Technology reported that the vendor incident behind the Cuyahoga County library’s app shutdown affected several library systems in the United States, and that the Perry Local School District in Stark County canceled classes on Monday, November 16, 2026, because of a cyber problem affecting the district’s technology systems. For Akron patrons, the practical effect is narrower but immediate: the app is down, and the account PIN or password is the credential the library is asking every cardholder to change.
What we know — and what we’re still waiting on: the library has confirmed which kinds of patron information were accessed, that its own databases and borrowing histories were not accessed, and that the access came through three account-services vendors. What has not been announced is how many cardholders were affected, when the library app will return, or what the vendors’ investigation ultimately finds as the cause.
What happens next: the vendors’ cybersecurity investigation continues, and patrons who have not yet done so are asked to reset their library account PIN or password — and, separately, their Libby and Hoopla credentials — while watching their accounts for unusual activity.
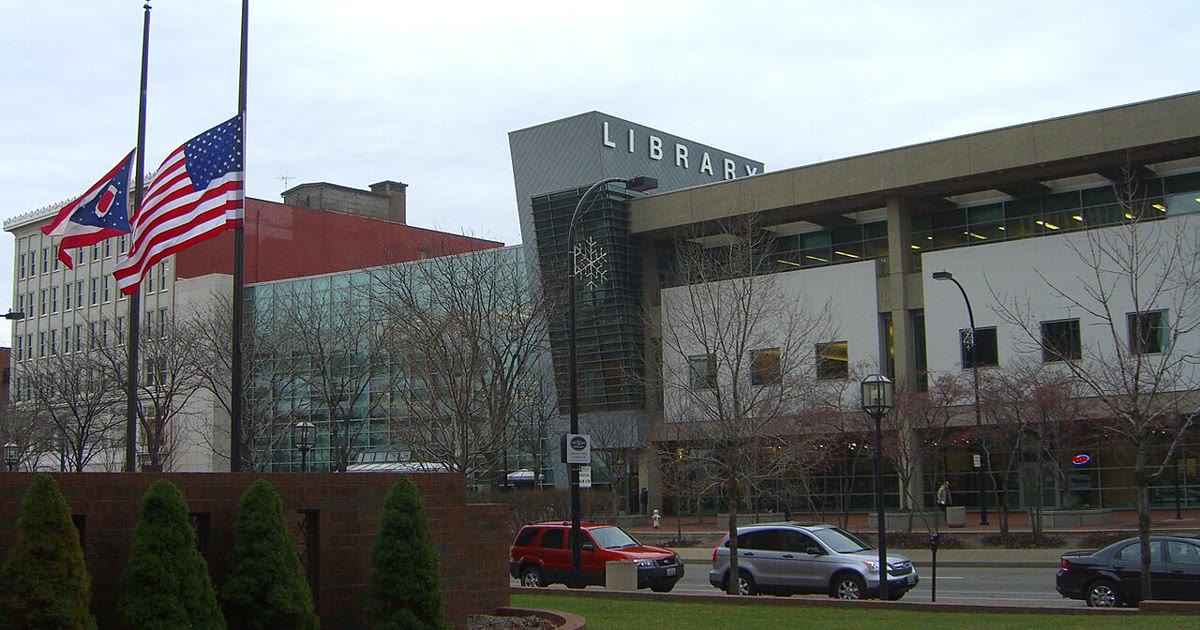
Photo: Nick81aku, CC BY